

Prerequisites
Before you begin, make sure you have:- Enabled OIDC in your env zero organization.
- Configured an Identity provider as explained in Set up an AWS OIDC authentication Guide.
Setup
To allow env zero to send logs to S3, you need an IAM policy with the necessary permissions. This policy will be attached to an IAM Role you use for OIDC authentication.The policy allows env zero to create and write to your S3 bucket.
Log Transporter Policy
Log Directory StructureLogs will be stored in your bucket with the following directory structure and file name format:
<bucketPath>/<logType>/<year>/<month>/<day>/<HH:mm:ss>_<5_random_chars>.log<bucketPath>: Your custom path (Optional)<logType>: Will be eitherenv0-deploymentsorenv0-auditsaccordingly
Self Configuration of S3 Transporter
There are two ways to configure the integrations: In the organization’s integrations page, click on Amazon S3 and fill the form’s fields: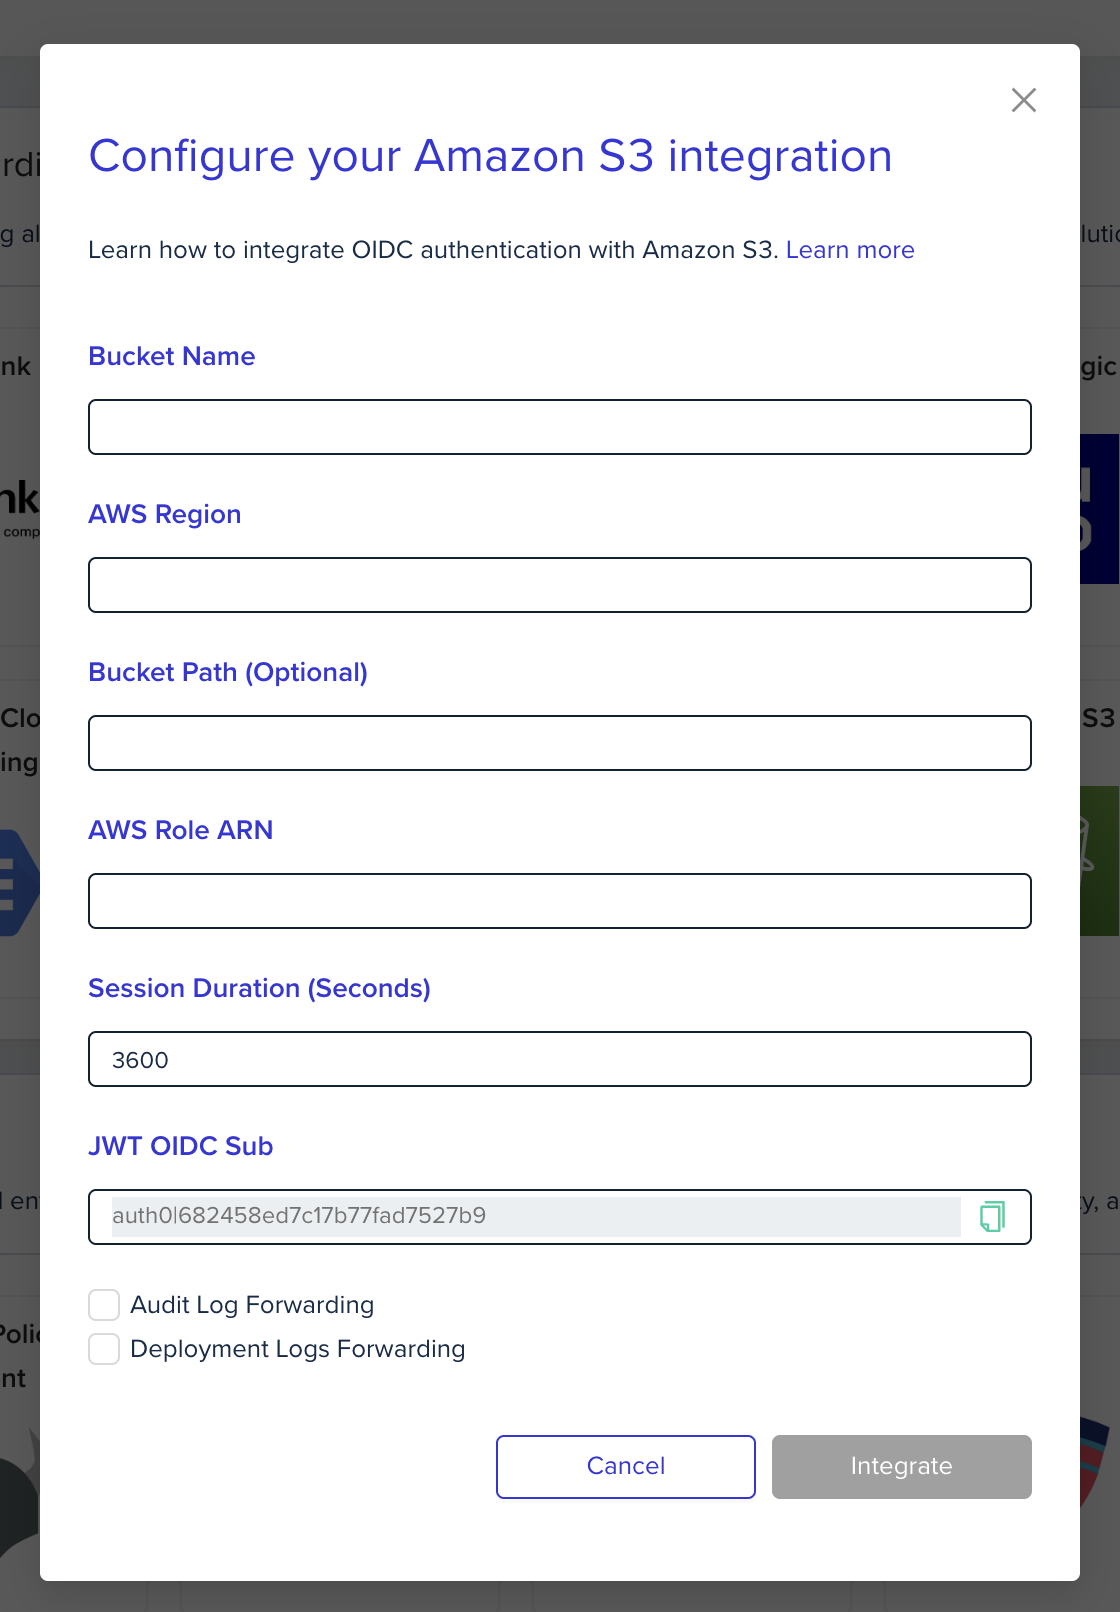
-
Using environment variables
In the env zero platform you will need to configure the following environment variables in any scope to forward the deployment logs. These are the relevant environment variables: